We find the gaps before attackers do.
AngelForce is a cyber security company in Tallinn, Estonia. We test, monitor and defend the systems of organisations across Europe.
- CEH
- LPT Master
- CISA
- Tallinn, Estonia · EU
What we do
Five areas of work, all of them security. Choose one to see what it covers, how we work and what you receive.
- 01 Penetration testing We attack your networks, applications and people the way a real adversary would, then show you how to close each gap.
- 02 Managed security Our security operations centre watches your environment around the clock and acts on threats before they become incidents.
- 03 Incident response When something goes wrong, we contain it, find the root cause and help you recover.
- 04 Consulting and training We assess where you stand, set priorities with you and train your staff to recognise attacks.
- 05 Secure software We build security into software from the first commit, and we build security tools of our own.
Free security tools
Eleven tools we use ourselves, free for everyone. Most run entirely in your browser, so what you enter stays with you.
- SecAudit seal verifier Check that a SecAudit security seal on a WordPress site is genuine, current and confirmed by its owner. Runs in your browser, asks a public service
- Email security check Grade a domain’s protection against spoofed email: SPF, DKIM, DMARC, DNSSEC, CAA and MTA-STS. Runs in your browser, asks a public service
- Security headers scanner Grade a website’s HTTP security headers, cookies and TLS certificate, with a fix for every finding. Our server fetches the page
- Phishing link analyser Paste a suspicious link or message and see where each link really leads, without opening it. Runs in your browser
- Password breach check Find out whether a password appears in known data breaches without revealing it. Runs in your browser, asks a public service
- SPF and DMARC generator Build correct SPF and DMARC records for your domain and check an existing SPF record. Runs in your browser
What happens in a penetration test
The same five steps, whether we test one web application or an entire organisation.
Scope
We agree on targets, rules and timing in writing. Nothing is tested without your approval.
Reconnaissance
We map what an attacker can see: domains, exposed services, technologies and people.
Exploitation
We try to get in with the techniques real attackers use, and stop at the limits we agreed.
Reporting
Every finding comes with its risk, the evidence and a concrete fix, plus a summary for management.
Retest
After you have fixed the issues, we test again and confirm that they are closed.
Our products
Besides our services we build software: one product makes WordPress sites faster, one shows whether they are secure, and Cortex runs penetration tests on its own.
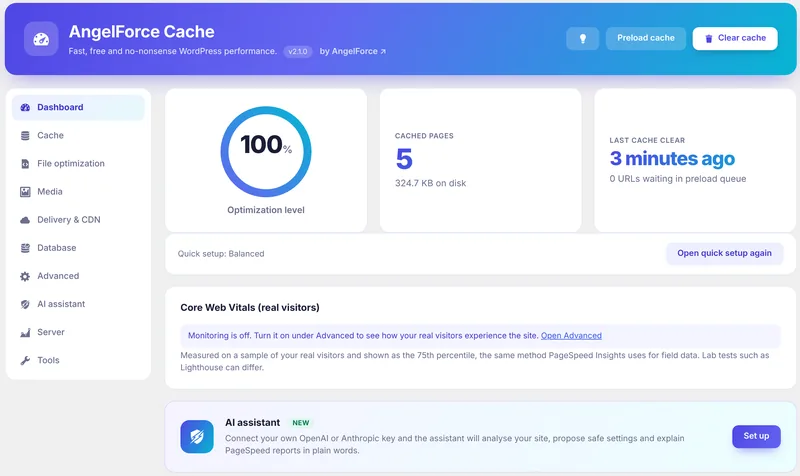
AngelForce Cache
AI Speed Optimizer for WordPress
Free WordPress speed plugin: page cache, minify, JavaScript delay, WebP/AVIF and an optional AI assistant for PageSpeed findings.
- PageSpeed, mobile and desktop
- 100
- Requests per second from cache
- 5,621
- Time to first byte
- 0.6 ms
-
Coming soon
SecAudit
Security audits for WordPress
Security audits for WordPress, built by AngelForce. SecAudit finds what puts a WordPress site at risk and turns it into evidence you can show to customers and auditors.
Learn more -
Coming soon
Cortex
Autonomous AI penetration testing
Autonomous penetration testing by AI agents, developed with AI models trained for offensive security.
Learn more
From the blog
Practical security writing for people who run systems: what to fix, in what order, and why.
-
Spotting password spraying and credential stuffing in your logs
How to recognise password spraying and credential stuffing in Microsoft 365 and web logins, and which lockout, MFA and alert settings stop them.
-
Find every device still sending mail with SMTP basic auth
How to find the scanners, printers, apps and scripts that still send mail through Exchange Online with a password, and what each should move to.
-
Password reset flows that do not undo your login security
How to design and test a forgot-password flow: tokens, expiry, enumeration, sessions, and a reset that cannot bypass an enrolled second factor.
Our certifications
Our consultants hold internationally recognised security certifications.
Check our own security
A security company should be able to show that its own house is in order. This site has no database, no login and no cookies, and it sends strict security headers. Verify it with the same public tools your auditors use.
- Security headers securityheaders.com
- TLS configuration Qualys SSL Labs
- Web security Mozilla Observatory
- Web and email standards Internet.nl
Tell us what you need to protect
Describe your environment and what you want to achieve. We will reply by email.
Contact us